Overview MetaDefender Sandbox API Reference Release Notes
Getting Started
Deployment & Usage
Support
Overview
3.0.0
Search this version
Layer 2 - Dynamic Analysis
Copy Markdown
Open in ChatGPT
Open in Claude
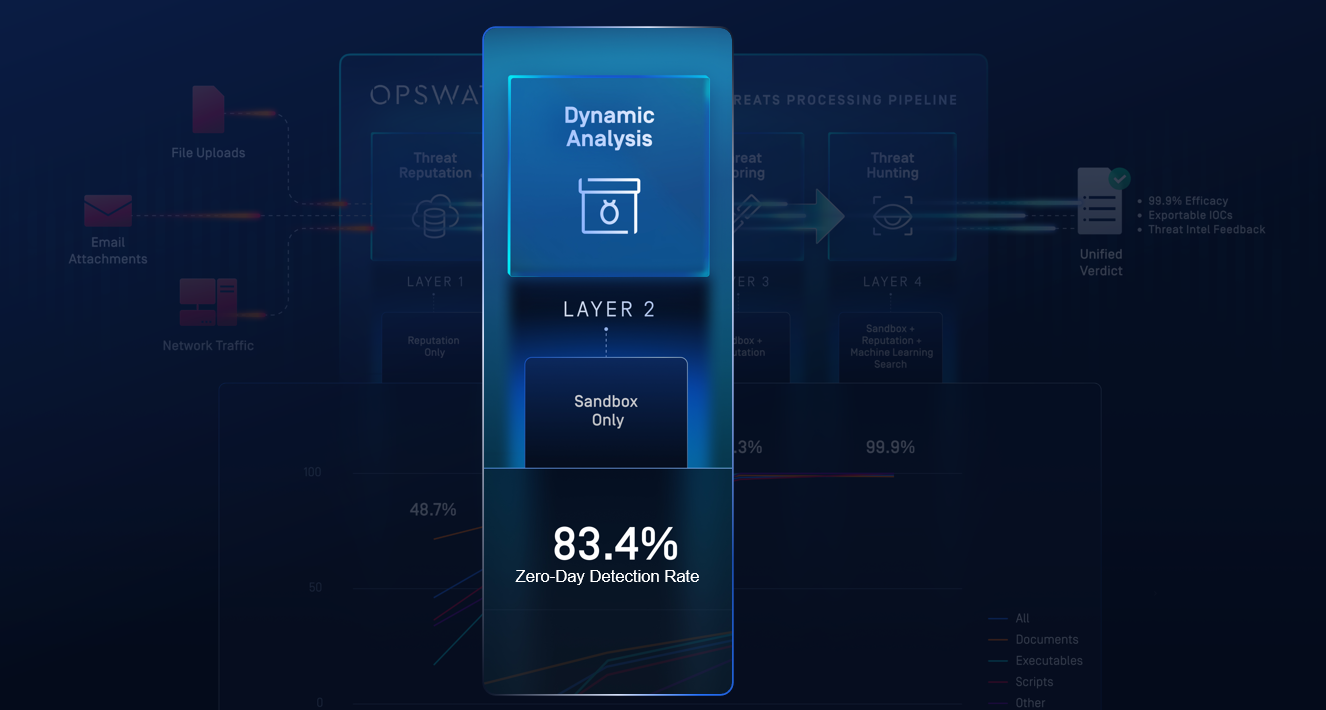
Unknown and suspicious files are executed in an emulation-based sandbox that bypasses anti-VM and timing-based evasion. Runtime behaviors, loader chains, scripts, and artifacts are exposed even when malware tries to stay dormant.
Last updated on
Was this page helpful?
Next to read:
Sandbox Engine FeaturesSee the "Technical Datasheet" for a complete list of features: https://docs.opswat.com/filescan/datasheet/technical-datasheet
Overview
Overview
Overview
Zero-Day Detection Pipeline